Cyber Security
Wyndham Exposed Customer Data After Leaving Database Password In Android App
Updated on Tue, Nov 10, 2026
Share
A password meant to protect customer information was embedded in Wyndham’s own Android app.
The hotel giant has revoked the exposed credential, but questions remain about who might have accessed its customer database before the security flaw was discovered.
TL;DR
- Security researcher Robert Wiggins discovered a database password embedded in Wyndham’s Android app, exposing access to an internal Salesforce-hosted system.
- Customer names, email addresses, rewards membership numbers, login tokens, and company documents were accessible.
- Wyndham revoked the credential after being alerted but has not disclosed the number of affected customers or whether they will receive notifications.
How A Password In Wyndham’s Android App Exposed Its Salesforce Customer Database
Security researcher Robert Wiggins discovered the vulnerability while examining Wyndham’s Android application code, as reported on November 9.
The application contained a hardcoded password that granted access to an internal company database hosted on Salesforce.
Essentially, anyone capable of extracting and examining the application's code could potentially retrieve the same credential and use it to access the connected database.
According to Wiggins, the database contained millions of entries, although he could not establish how many individual customer records were exposed.
Interestingly, Wyndham has approximately 129 million enrolled rewards members, although this figure does not represent the number of customers affected by the vulnerability.
Beyond customer names, email addresses, and membership numbers, the exposed database stored JSON Web Tokens (JWTs), which allow customers to remain signed in without repeatedly entering their passwords.
Company files and documents were also accessible. However, the discovery does not establish that customer information was stolen or misused.
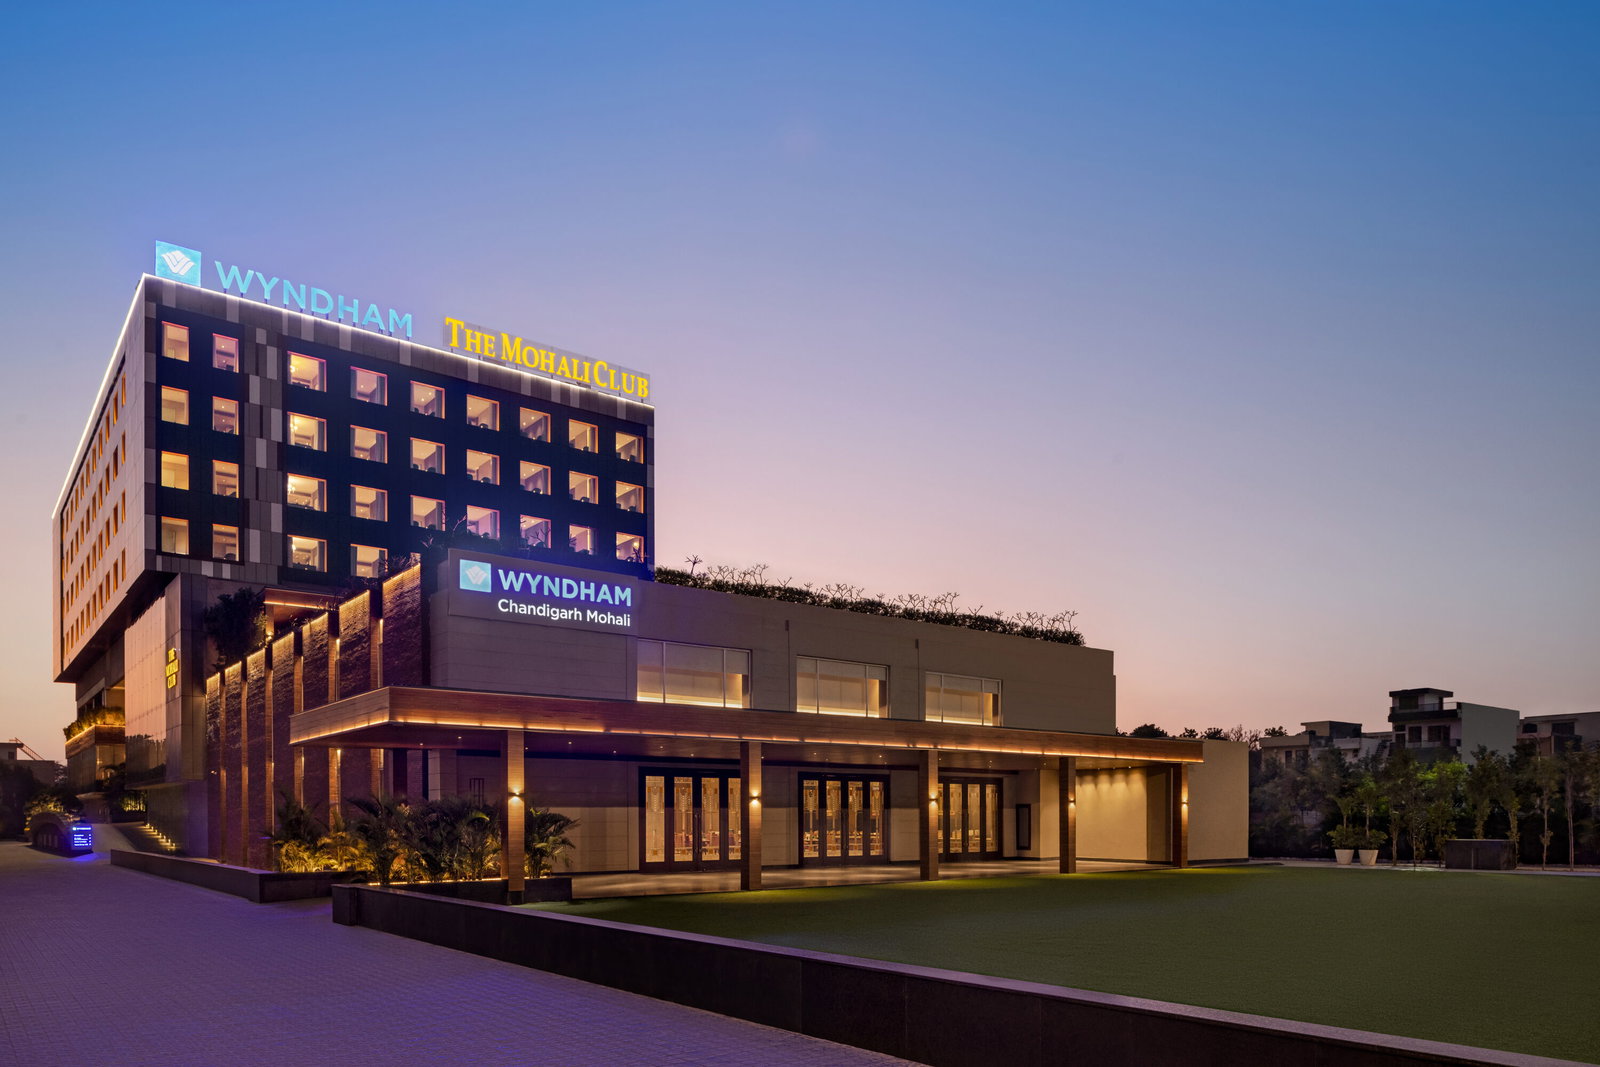
Researcher's Alert Prompts Wyndham To Revoke Exposed Database Credential
Wiggins said Wyndham lacked a clear mechanism for privately reporting security vulnerabilities, prompting him to seek TechCrunch's assistance in contacting the company.
Following the publication's outreach to Wyndham's cybersecurity team, the exposed credential was revoked, preventing further access through that password.
Interestingly, this was the researcher's second discovery of a similar vulnerability within two weeks, having previously identified hardcoded credentials in Applebee's application.
Both discoveries involved AI tools capable of examining thousands of lines of decompiled application code to identify security weaknesses.
The incident also highlights how overlooked credentials can expose customer information, an issue relevant to TechDogs' coverage of AI-assisted cybersecurity research and customer-data security incidents in the travel industry.
However, revoking a compromised credential does not necessarily establish whether someone accessed the database before the vulnerability was reported.
Topics For More Insights
Wyndham Leaves Questions About Customer Notifications And App Security Unanswered
Following the discovery, a Wyndham spokesperson told TechCrunch, “Our team has taken steps to address the issue.”
The company also stated, “Our security teams have no evidence of any unauthorized access.”
However, Wyndham declined to clarify whether it possessed server logs or other technical records capable of identifying earlier access to the database.
It also did not confirm whether affected customers would be notified, whether the incident would be disclosed to US regulators, or how it planned to implement a permanent fix for the Android application.
Furthermore, Wyndham cybersecurity director Michael Francess provided an email contact for researchers to report potential vulnerabilities, although the company did not commit to establishing a formal vulnerability disclosure program.
The development follows a separate security incident in 2024, when spyware installed on some Wyndham hotel check-in computers exposed screenshots containing guest records and booking information.
For now, the exposed password has been revoked, but the duration of the vulnerability, the number of potentially affected customers, and any unauthorized access remain unresolved.
First published on Tue, Nov 10, 2026

Liked what you read? That’s only the tip of the tech iceberg!
Explore our vast collection of tech articles including introductory guides, product reviews, trends and more, stay up to date with the latest news, relish thought-provoking interviews and the hottest AI blogs, and tickle your funny bone with hilarious tech memes!
Plus, get access to branded insights from industry-leading global brands through informative white papers, engaging case studies, in-depth reports, enlightening videos and exciting events and webinars.
Dive into TechDogs' treasure trove today and Know Your World of technology like never before!
Disclaimer - Reference to any specific product, software or entity does not constitute an endorsement or recommendation by TechDogs nor should any data or content published be relied upon. The views expressed by TechDogs' members and guests are their own and their appearance on our site does not imply an endorsement of them or any entity they represent. Views and opinions expressed by TechDogs' Authors are those of the Authors and do not necessarily reflect the view of TechDogs or any of its officials. While we aim to provide valuable and helpful information, some content on TechDogs' site may not have been thoroughly reviewed for every detail or aspect. We encourage users to verify any information independently where necessary.
Loading comments...