Cyber Security
BlackBerry Lifts FY2026 Outlook As Microsoft Hardens M365, Ransomware Case
Updated on Mon, Dec 22, 2025
Share
Here’s what’s in the news.
BlackBerry raised the lower end of its annual revenue outlook due to demand for its cybersecurity software; Microsoft began rolling out a new Baseline Security Mode to help organizations harden Microsoft 365 faster; and two former cybersecurity professionals pleaded guilty to allegedly running ransomware attacks on U.S. businesses.
TL; DR
-
BlackBerry lifted its FY2026 revenue outlook as demand for cybersecurity software increased across enterprises and automotive-linked QNX deployments.
-
Microsoft launched Baseline Security Mode for Microsoft 365 to simplify risk assessment and enforce secure-by-default protections.
-
Former cybersecurity professionals pleaded guilty to ransomware extortion, highlighting persistent insider threats despite stronger security measures.
What Did BlackBerry Update In Its Forecast?
BlackBerry raised the lower end of its fiscal 2026 revenue forecast, signaling stronger demand for its cybersecurity software as organizations spend more to counter increasingly sophisticated attacks.
The company now expects annual revenue of $531M to $541M, up from its prior range of $519M to $541M. Also, BlackBerry has reported Q3 revenue of $141.8M (quarter ended November 30, 2025), above analyst estimates of $137.4M (LSEG).
Its QNX embedded software business continued to expand, with BlackBerry stating that more than 275M vehicles globally now use QNX technology.
QNX segment revenue rose 10% year-over-year to $68.7M for the reported quarter.
For fiscal Q4, BlackBerry expects revenue between $138M and $148M, with the midpoint broadly in line with estimates cited by Reuters.
While BlackBerry’s financial performance reflects rising cybersecurity demand, platform-level changes are also reshaping how organizations like Microsoft approach baseline protection.
What Is Microsoft’s Baseline Security Mode For Microsoft 365?
Microsoft has begun deploying Baseline Security Mode in the Microsoft 365 admin center, a guided dashboard that centralizes recommended security configurations across Office, Exchange, Teams, SharePoint/OneDrive, and Microsoft Entra.
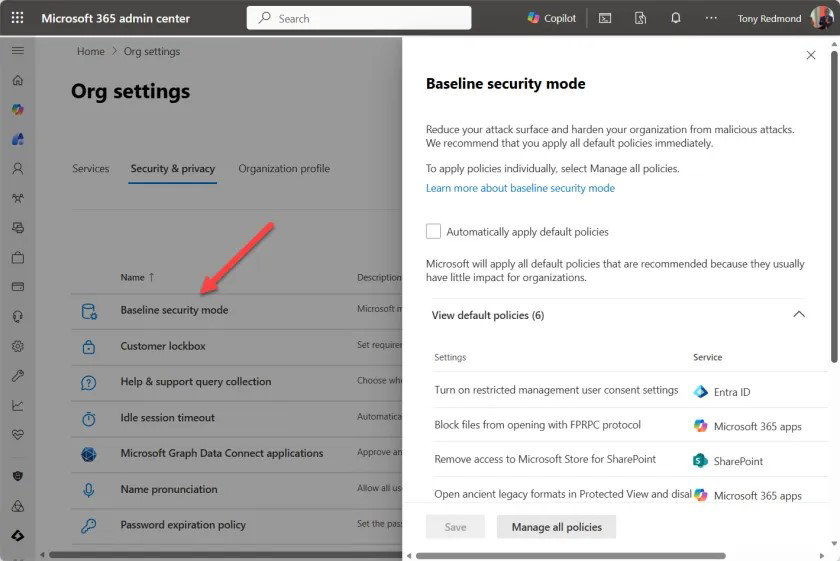
Microsoft positions this as a faster way for admins to identify gaps, simulate changes, and deploy protections, while maintaining a more consistent security posture across M365 services.
The feature is designed to help organizations apply settings that previously required more manual work (often via scripting/PowerShell), while still allowing teams to evaluate the impact before deployment.
Microsoft’s official materials describe Baseline Security Mode as covering multiple configuration areas (including authentication and file-related controls) and being available through a guided admin experience.
Microsoft recommends using impact reporting to identify dependencies first, then turning on settings where impact is minimal or manageable, aiming for a “secure-by-default” posture without surprise disruption.
Even as vendors push for stronger defaults and proactive hardening, recent criminal cases highlight how insider knowledge can still be exploited for malicious gain.
Topics For More Insights
What Happened In The Ransomware Guilty Pleas Case?
Two former cybersecurity professionals, Ryan Clifford Goldberg and Kevin Tyler Martin, pleaded guilty to federal charges connected to launching ransomware attacks against U.S. businesses, according to reporting on the case.
Coverage states they admitted to a conspiracy involving extortion, with prosecutors alleging they used their insider knowledge to target victims over multiple incidents.
Reporting around the broader case has linked activity to the ALPHV/BlackCat ransomware ecosystem in prior filings and coverage.
“They acted wholly outside the scope of their employment and without any authorization, knowledge, or involvement from the company,” said a spokesperson at DigitalMint in an emailed statement.
Also, a spokesperson for the Israel-based firm Sygnia confirmed that Goldberg was fired “immediately upon learning of the situation.” Sygnia emphasized that the firm itself is not a target of the investigation.
So, with all that, do you think “secure-by-default” rollouts like Microsoft’s Baseline Security Mode will meaningfully reduce misconfigurations, or will attacker incentives keep shifting faster than orgs can harden?
Let us know in the comments below!
First published on Mon, Dec 22, 2025

Enjoyed what you read? Great news – there’s a lot more to explore!
Dive into our content repository of the latest tech news, a diverse range of articles spanning introductory guides, product reviews, trends and more, along with engaging interviews, up-to-date AI blogs and hilarious tech memes!
Also explore our collection of branded insights via informative white papers, enlightening case studies, in-depth reports, educational videos and exciting events and webinars from leading global brands.
Head to the TechDogs homepage to Know Your World of technology today!
Disclaimer - Reference to any specific product, software or entity does not constitute an endorsement or recommendation by TechDogs nor should any data or content published be relied upon. The views expressed by TechDogs' members and guests are their own and their appearance on our site does not imply an endorsement of them or any entity they represent. Views and opinions expressed by TechDogs' Authors are those of the Authors and do not necessarily reflect the view of TechDogs or any of its officials. While we aim to provide valuable and helpful information, some content on TechDogs' site may not have been thoroughly reviewed for every detail or aspect. We encourage users to verify any information independently where necessary.
Loading comments...